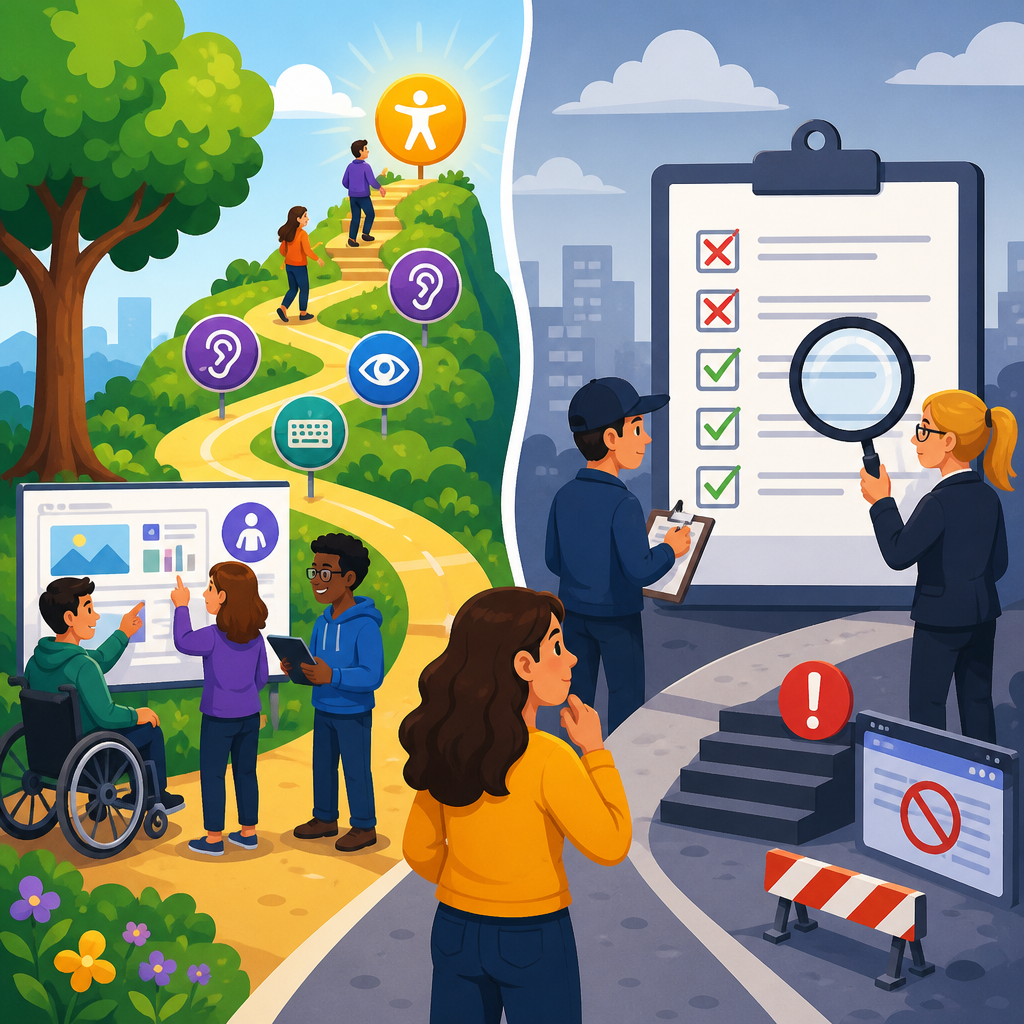
Accessibility maturity assessments and compliance audits both evaluate digital accessibility, but they answer different business questions, require different evidence, and lead to different action plans. Teams often treat them as interchangeable because both involve reviewing websites, apps, documents, and design systems against accessibility expectations. In practice, a compliance audit asks, “Do we meet defined requirements right now?” while a maturity assessment asks, “How capable are we of producing and sustaining accessible experiences over time?” That distinction matters for any organization working on ADA audits and compliance tools, because legal exposure and operational capability are related, but not identical.
In my work with product, design, and governance teams, the biggest source of confusion appears when an executive sees a score from one exercise and assumes it describes the other. A clean audit result does not prove that future releases will stay accessible. A strong maturity rating does not mean the current site is free of barriers. Understanding both methods helps organizations set realistic priorities, allocate budget correctly, and avoid the common cycle of fixing issues late, then recreating them in the next release.
For this hub page under compliance and implementation, it helps to define the core terms clearly. A compliance audit is a structured review of digital assets against a standard or legal expectation, most often WCAG 2.1 or WCAG 2.2 at Level A and AA, sometimes mapped to Section 508, EN 301 549, or organizational policy. An accessibility maturity assessment reviews people, process, governance, tooling, procurement, content operations, design practice, development workflows, quality assurance, training, and measurement. It examines whether accessibility is built into the organization rather than bolted on at the end.
Why does this difference matter now? Because ADA-related claims, procurement scrutiny, and customer expectations are all increasing, while digital estates are becoming more complex. A company may have a marketing site, authenticated application, mobile app, PDF library, support chatbot, and third-party integrations. Auditing every asset can reveal current defects, but only maturity work explains why those defects recur. Conversely, maturity programs without baseline audits can create false confidence. The most effective accessibility strategy uses both: audits to identify barriers and legal risk, and maturity assessments to improve the system that produces digital experiences.
What a compliance audit is designed to measure
A compliance audit measures conformance at a point in time. The objective is to determine whether a specific website, app, document set, kiosk flow, or design system component meets defined success criteria. Most digital accessibility audits are anchored in WCAG because it provides testable requirements across perceivable, operable, understandable, and robust content. Auditors inspect templates, user journeys, components, forms, media, error handling, keyboard support, focus order, semantics, name-role-value exposure, contrast, zoom behavior, and screen reader announcements. Findings are usually documented by severity, affected users, code location, and relevant success criterion.
Good audits combine automated scanning with manual expert testing. Automated tools such as axe DevTools, WAVE, ARC Toolkit, Siteimprove, Deque WorldSpace, Google Lighthouse, and Accessibility Insights can detect recurring issues like missing alternative text, empty buttons, insufficient landmark structure, color contrast failures, and invalid ARIA usage. However, automation typically captures only a fraction of WCAG failures. A reliable audit also includes keyboard-only testing, screen reader testing with tools like NVDA, JAWS, and VoiceOver, responsive reflow checks, magnification review, and examination of dynamic components such as modals, menus, carousels, and custom widgets.
The output of a compliance audit is usually tactical. It produces a defect log, a conformance summary, a risk view, and remediation recommendations. If the scope is broad, it may also include a representative sample methodology, because large digital estates cannot always be tested page by page. For ADA audits and compliance tools, this is the practical center of the work: identify barriers, show evidence, prioritize fixes, and support legal, procurement, or release decisions. An audit is not merely a checklist exercise when done correctly; it is a structured body of evidence about user impact and conformance status.
What an accessibility maturity assessment is designed to measure
An accessibility maturity assessment measures organizational capability rather than asset-level conformance. Instead of asking whether a page passes Success Criterion 1.4.3 for contrast or 2.4.7 for focus visible, it asks whether brand standards, design tokens, component libraries, coding practices, and quality gates make those outcomes likely across products. The assessment looks at governance, ownership, policy, training, budgeting, procurement language, vendor management, issue intake, remediation workflows, and executive reporting. It also examines whether accessibility is considered in discovery, research, content creation, sprint planning, definition of done, and post-release monitoring.
I usually explain maturity using a simple idea: audits inspect the product, maturity assessments inspect the production system. A team may earn reasonable audit results because a few specialists manually fixed a release. That does not scale. Mature organizations distribute accessibility responsibilities across roles. Designers understand focus indicators and error prevention. Engineers use semantic elements before custom ARIA. QA includes keyboard and assistive technology checks in standard test plans. Procurement requires VPAT review and validation for third-party software. Content teams know heading structure, link purpose, and caption requirements. Leadership tracks accessibility with the same seriousness as security or privacy.
Several models support this work, including the W3C Accessibility Maturity Model. Organizations may adapt dimensions and scoring scales, but the strongest assessments use observable evidence instead of opinion alone. Evidence can include policy documents, design system guidance, training completion data, pull request templates, CI pipeline checks, bug taxonomy, procurement standards, governance charters, support escalation procedures, and roadmaps with funded ownership. The deliverable is strategic: current-state capability, target-state recommendations, sequencing, and change management priorities. It tells leaders where to invest so accessibility becomes repeatable, measurable, and durable.
Accessibility maturity assessments vs compliance audits: the practical differences
The simplest way to compare the two is by purpose, scope, timing, and outputs. A compliance audit is usually narrow enough to be testable and evidence-based at the interface level. A maturity assessment is broader and examines how decisions are made across teams. One identifies current barriers; the other identifies the conditions that create or prevent those barriers. Both are necessary, but they should not be procured, staffed, or reported as though they were the same service.
| Area | Compliance Audit | Maturity Assessment |
|---|---|---|
| Primary question | Does this asset conform to required standards now? | Can this organization consistently produce accessible outcomes? |
| Typical scope | Website, app, documents, user journeys, components | Governance, roles, process, tooling, training, procurement |
| Main standards | WCAG 2.1/2.2, Section 508, EN 301 549, policy baselines | Internal maturity model, W3C guidance, operating model criteria |
| Methods | Manual testing, assistive technology testing, automated scans | Interviews, artifact review, workflow analysis, capability scoring |
| Output | Findings log, severity ranking, remediation guidance, conformance view | Capability gaps, roadmap, ownership model, investment priorities |
| Best use | Risk reduction, release decisions, litigation response, procurement validation | Program building, sustainable implementation, executive planning |
Real-world examples make the difference clearer. If a retailer is preparing for a demand letter response, it needs an audit of critical shopping flows, account creation, checkout, and customer support touchpoints. If the same retailer has repeated contrast, focus, and form-label problems across brands, it needs a maturity assessment to review design system governance, QA coverage, and release management. If a university is buying a new learning platform, a compliance audit can validate the vendor’s claims. If the university wants to improve accessibility across web, mobile, PDF, and video operations, a maturity assessment will expose where policy and process are failing.
How ADA audits and compliance tools fit into the picture
ADA audits and compliance tools sit primarily on the compliance side, but their value depends on how they are used. Tools are accelerators, not substitutes for expertise. Enterprise scanners can identify patterns across thousands of pages, estimate issue prevalence, and support ongoing monitoring. Browser extensions help developers inspect names, roles, labels, heading structure, tab order, and contrast during implementation. Document checkers can flag missing tags or reading-order concerns in PDFs. Yet none of these tools can fully judge context, meaning, task completion, or whether a custom interaction is understandable with assistive technology. Human review remains essential.
For hub-level planning, it helps to group tools by purpose. Discovery tools crawl sites and surface obvious defects at scale. Developer tools support component-level debugging during build. QA tools aid repeatable regression testing. Program dashboards track issue trends, ownership, and closure over time. Legal and procurement workflows may add VPAT review templates, exception registers, and remediation attestations. The strongest organizations connect these layers instead of buying isolated products. For example, CI checks may catch low-level markup problems before merge, while scheduled scans monitor production drift and manual audits validate critical flows before major releases.
There is also an important limitation to understand in ADA work: the Americans with Disabilities Act does not publish a technical checklist for websites in the way WCAG does. In practice, organizations map ADA expectations to recognized technical standards, usually WCAG Level AA, and pair that with user-impact evidence. That is why compliance tools should be presented honestly. They can support defensible effort, but they do not certify legal immunity. Any vendor promising a guaranteed lawsuit shield through a widget, overlay, or scan-only platform should be treated skeptically. Courts, users, and regulators care about actual accessibility, not marketing language.
When to choose one, when to use both, and how to sequence the work
Choose a compliance audit when you need to know the current accessibility status of a digital asset, especially before launch, after a complaint, during procurement, after a redesign, or when preparing a remediation plan. Choose a maturity assessment when accessibility problems are recurring across teams, when ownership is unclear, when executives need a program roadmap, or when the organization wants to scale from reactive fixes to sustained implementation. Most enterprises eventually need both, and the best results come from sequencing them intentionally rather than commissioning them as isolated projects.
A practical sequence usually starts with a scoped compliance audit of the highest-risk experiences: core customer journeys, revenue pathways, support channels, and high-volume templates. That gives immediate visibility into barriers and legal exposure. Next, conduct a maturity assessment to understand why those barriers exist and which organizational changes will reduce recurrence. Then create an integrated roadmap with parallel tracks: remediate critical defects, improve design system patterns, update development standards, train role-specific teams, strengthen procurement language, and establish governance metrics. This sequence balances urgent risk reduction with long-term capability building.
Success depends on reporting the two workstreams differently. Audit reporting should focus on affected journeys, severity, standards references, reproducibility, and remediation owners. Maturity reporting should focus on capability levels, operating model gaps, dependencies, investment needs, and measurable milestones. Do not collapse these into a single blended score. A board or executive team needs to know whether the organization has a current product problem, a systems problem, or both. Clear separation improves budget decisions and prevents the common mistake of celebrating process improvements while unresolved user barriers remain in production.
Common mistakes organizations make
The first mistake is assuming that automated scans equal an audit. They do not. Scan data is useful, but it misses issues involving keyboard traps, screen reader context, meaningful sequence, accessible names that do not match visible labels, timing, motion triggers, and many dynamic interaction failures. The second mistake is commissioning a one-time audit with no remediation governance. Findings without ownership, target dates, and regression prevention simply create a backlog. The third mistake is treating accessibility as a specialist function only. Lasting performance requires role-based accountability across product management, design, engineering, QA, content, legal, procurement, and support.
Another frequent problem is misunderstanding sampling. Large sites and applications often rely on representative templates and user flows. That is reasonable, but weak sampling can miss high-risk exceptions such as account settings, embedded support tools, regional pages, or legacy documents. Teams also underestimate third-party exposure. Payment providers, chat widgets, scheduling tools, maps, and identity platforms can create significant barriers even when the host site is well built. Finally, some organizations launch broad maturity programs with no baseline audit evidence. Without concrete findings tied to user journeys, strategic recommendations can feel abstract and struggle to secure funding.
The key takeaway is straightforward: compliance audits and accessibility maturity assessments are complementary, not competing, practices. Audits tell you whether users face barriers in specific digital experiences today. Maturity assessments tell you whether your organization is equipped to prevent those barriers tomorrow. For any business building an ADA audits and compliance tools strategy, that distinction is the foundation of smart planning. It keeps legal risk, user experience, and operational improvement aligned instead of forcing one initiative to do every job badly.
If you manage a digital portfolio, start by inventorying your highest-risk assets and selecting a standards-based audit approach that includes manual testing. Then evaluate the broader system: governance, training, design system coverage, procurement controls, and release gates. Use the audit to prioritize remediation, and use the maturity assessment to stop defects from recurring. That combination delivers the real benefit organizations need: not a one-time pass/fail snapshot, but a sustainable accessibility program that improves customer experience, supports compliance, and strengthens implementation across every release. Build your roadmap, assign owners, and begin with the journeys users rely on most.
Frequently Asked Questions
What is the main difference between an accessibility maturity assessment and a compliance audit?
The core difference is the business question each one is designed to answer. A compliance audit is a point-in-time evaluation that asks whether a website, app, document set, or design system currently meets defined accessibility requirements, usually against standards such as WCAG and, in some cases, legal or contractual obligations. It is focused on present-state conformance. The output is typically a list of issues, their severity, the criteria affected, and remediation guidance so teams can fix barriers and reduce risk.
An accessibility maturity assessment looks much broader and deeper. Instead of asking only whether current experiences pass or fail, it examines whether the organization has the internal capability to consistently build, buy, test, and maintain accessible digital products over time. That means reviewing governance, policies, roles and responsibilities, procurement practices, design and development workflows, testing methods, training, leadership support, metrics, and continuous improvement. In short, a compliance audit tells you how accessible something is today, while a maturity assessment tells you how likely your organization is to produce accessible outcomes consistently in the future.
That distinction matters because two organizations can have similar audit results but very different maturity levels. One might have passed because of a one-time cleanup project, while the other has accessibility embedded into product lifecycle processes. The first organization may quickly fall out of compliance again, while the second is much better positioned to sustain progress. For that reason, the two activities are complementary, not interchangeable.
When should an organization choose a compliance audit instead of a maturity assessment?
An organization should prioritize a compliance audit when it needs a clear answer about current conformance status. This is especially important before a product launch, during vendor evaluation, in response to customer complaints, before litigation exposure increases, when preparing accessibility statements, or when leadership needs a defensible understanding of present risk. If the immediate question is, “Where are the accessibility barriers right now, and what must we fix first?” then a compliance audit is the right tool.
Compliance audits are also useful when teams need specific, testable findings tied to recognized standards. For example, a product team may need to verify whether checkout flows, authentication, mobile navigation, PDFs, or video players meet required success criteria. In those situations, the organization needs concrete evidence from manual testing, assistive technology checks, keyboard review, code inspection, and issue documentation. A maturity assessment does not replace that level of product-specific validation.
That said, choosing an audit does not mean maturity is irrelevant. It simply means the organization’s immediate need is tactical rather than strategic. If a team has repeated audit failures, recurring regressions, or an ongoing pattern of inaccessible releases, that is often a sign that a maturity assessment should follow. The audit identifies the symptoms in the product; the maturity assessment investigates the operational causes behind those symptoms.
What kinds of evidence are reviewed in a maturity assessment versus a compliance audit?
The evidence is different because the purpose is different. In a compliance audit, the evidence is primarily product-focused. Reviewers examine live pages, templates, application screens, user flows, document samples, design components, and interactive elements. They test against defined criteria using a combination of automated scanning, manual evaluation, keyboard-only navigation, screen reader testing, zoom and reflow checks, form validation review, multimedia assessment, and often mobile or cross-browser verification. The evidence is direct and observable: either the experience meets the requirement, partially meets it, or fails it.
In a maturity assessment, the evidence is organizational and process-oriented. Reviewers typically look at accessibility policies, governance documents, procurement requirements, design standards, coding guidelines, QA procedures, issue-tracking practices, release gates, training programs, hiring expectations, vendor management processes, and internal escalation paths. They also gather evidence through interviews and workshops with leadership, designers, developers, testers, content authors, legal teams, procurement specialists, and support staff. The question is not just whether a product is accessible today, but whether the organization has repeatable mechanisms to produce accessible outcomes at scale.
Another key difference is how findings are framed. Audit evidence leads to issue-level findings such as missing form labels, low color contrast, improper heading structure, inaccessible modals, or unlabeled buttons. Maturity evidence leads to capability-level findings such as inconsistent design system adoption, lack of accessibility acceptance criteria in agile workflows, insufficient training for content authors, no procurement checkpoints for third-party tools, or unclear executive ownership. Both forms of evidence are valuable, but they inform very different action plans.
What deliverables and action plans come out of each type of assessment?
A compliance audit usually produces a remediation-focused deliverable. This often includes an executive summary, testing methodology, scope, standards used, detailed findings mapped to relevant criteria, severity ratings, examples of user impact, and recommended fixes. Some audits also include screenshots, code snippets, reproducing steps, and prioritized remediation roadmaps. The resulting action plan is generally short- to medium-term: fix critical barriers, address high-impact issues, validate repairs, and establish a process for retesting before release or publication.
A maturity assessment produces a transformation-focused deliverable. Instead of centering only on defects, it typically describes the organization’s current accessibility capability across multiple dimensions, such as leadership commitment, governance, procurement, design, engineering, QA, content operations, support, and measurement. It may assign maturity levels to each area, identify strengths and gaps, and recommend a staged roadmap for improvement. That roadmap often includes creating standards, clarifying ownership, embedding accessibility into workflows, improving training, strengthening design systems, building testing practices, and defining metrics for accountability.
The difference in action plans is significant. Audit remediation is about correcting barriers in digital products. Maturity improvement is about changing how the organization works so those barriers become less frequent and easier to catch earlier. In mature programs, audit findings become inputs into continuous improvement rather than isolated clean-up projects. Ideally, organizations use both deliverables together: the audit to solve immediate product issues and the maturity roadmap to prevent the same categories of issues from recurring.
Can a company be compliant today but still have low accessibility maturity?
Yes, and this is one of the most common misunderstandings in digital accessibility. A company can achieve acceptable audit results on a website or application and still have low maturity if accessibility depends on a small number of specialists, a one-time remediation effort, or last-minute QA checks. In that situation, the current product may appear compliant, but the organization lacks the structures needed to maintain accessibility as content changes, features evolve, teams rotate, and new vendors are introduced.
Low maturity often shows up through patterns such as accessibility being addressed late in the development cycle, inconsistent design decisions across teams, no formal training for authors or engineers, limited executive oversight, weak procurement controls, or no accessibility requirements in definitions of done. These gaps may not always be obvious in a single audit, especially if a product was heavily remediated just before review. But they become visible over time through regressions, duplicate issue types, slow remediation, and uneven accessibility quality across channels.
The reverse can also happen in a limited sense: an organization may be building strong maturity but still have current compliance gaps because it is early in its improvement journey or managing legacy systems. That is why smart accessibility programs do not rely on a single measure of success. They track both outcome indicators, such as audit results and user-reported barriers, and capability indicators, such as training completion, design system coverage, procurement controls, and accessibility checkpoints in delivery processes. Sustainable accessibility comes from combining present-state compliance with long-term organizational maturity.